Resources
Guides
Plain-language guides to the rules organizations ask us about for compliance and security programs.
Plain-language guides to the rules organizations ask us about for compliance and security programs.
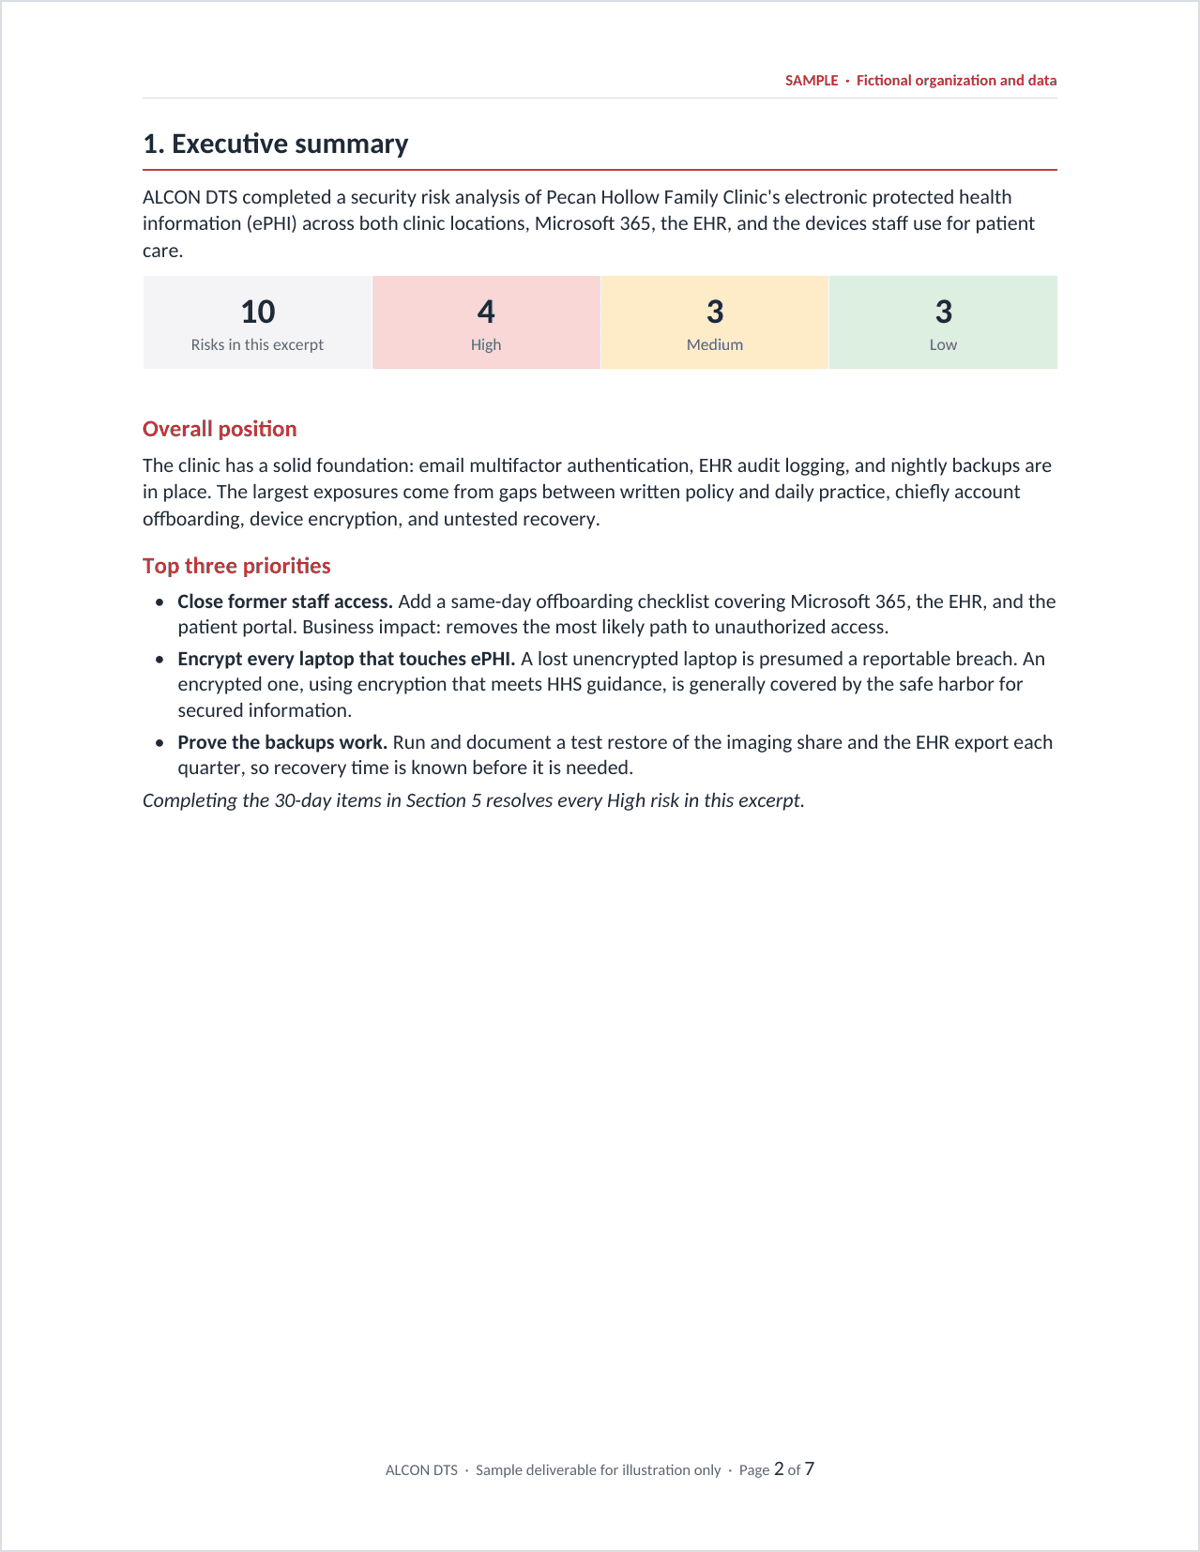
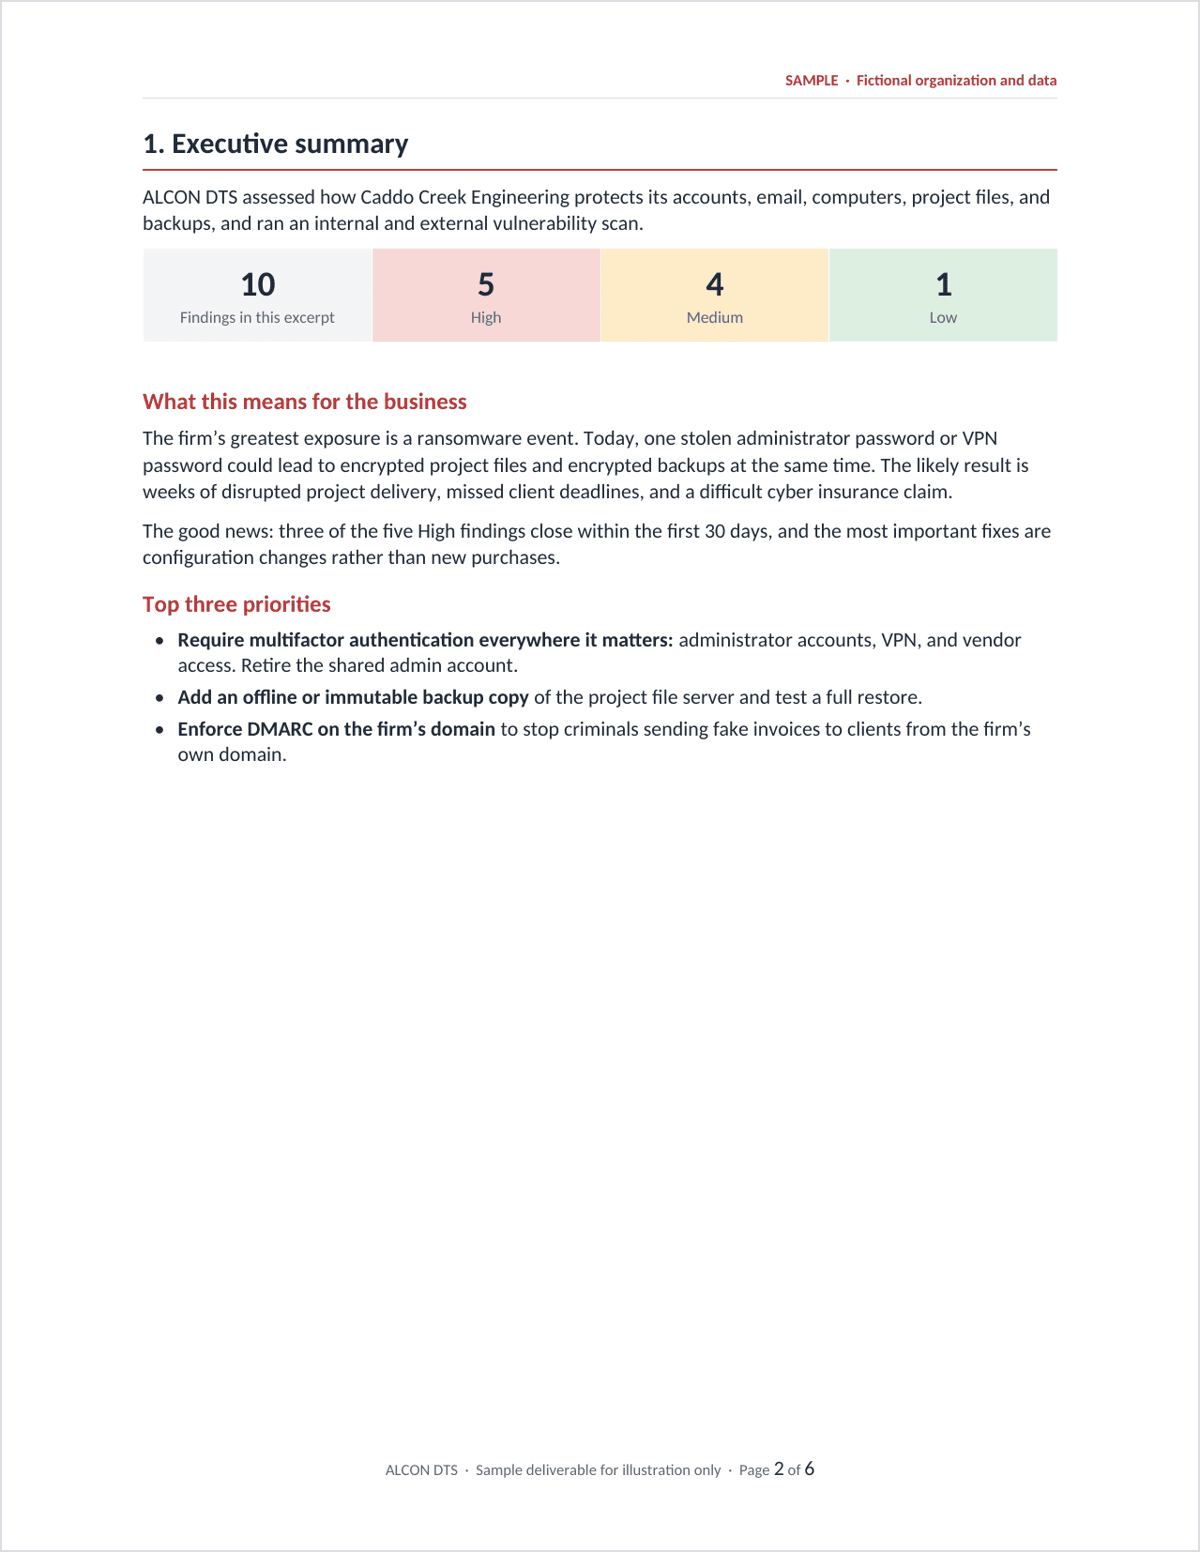
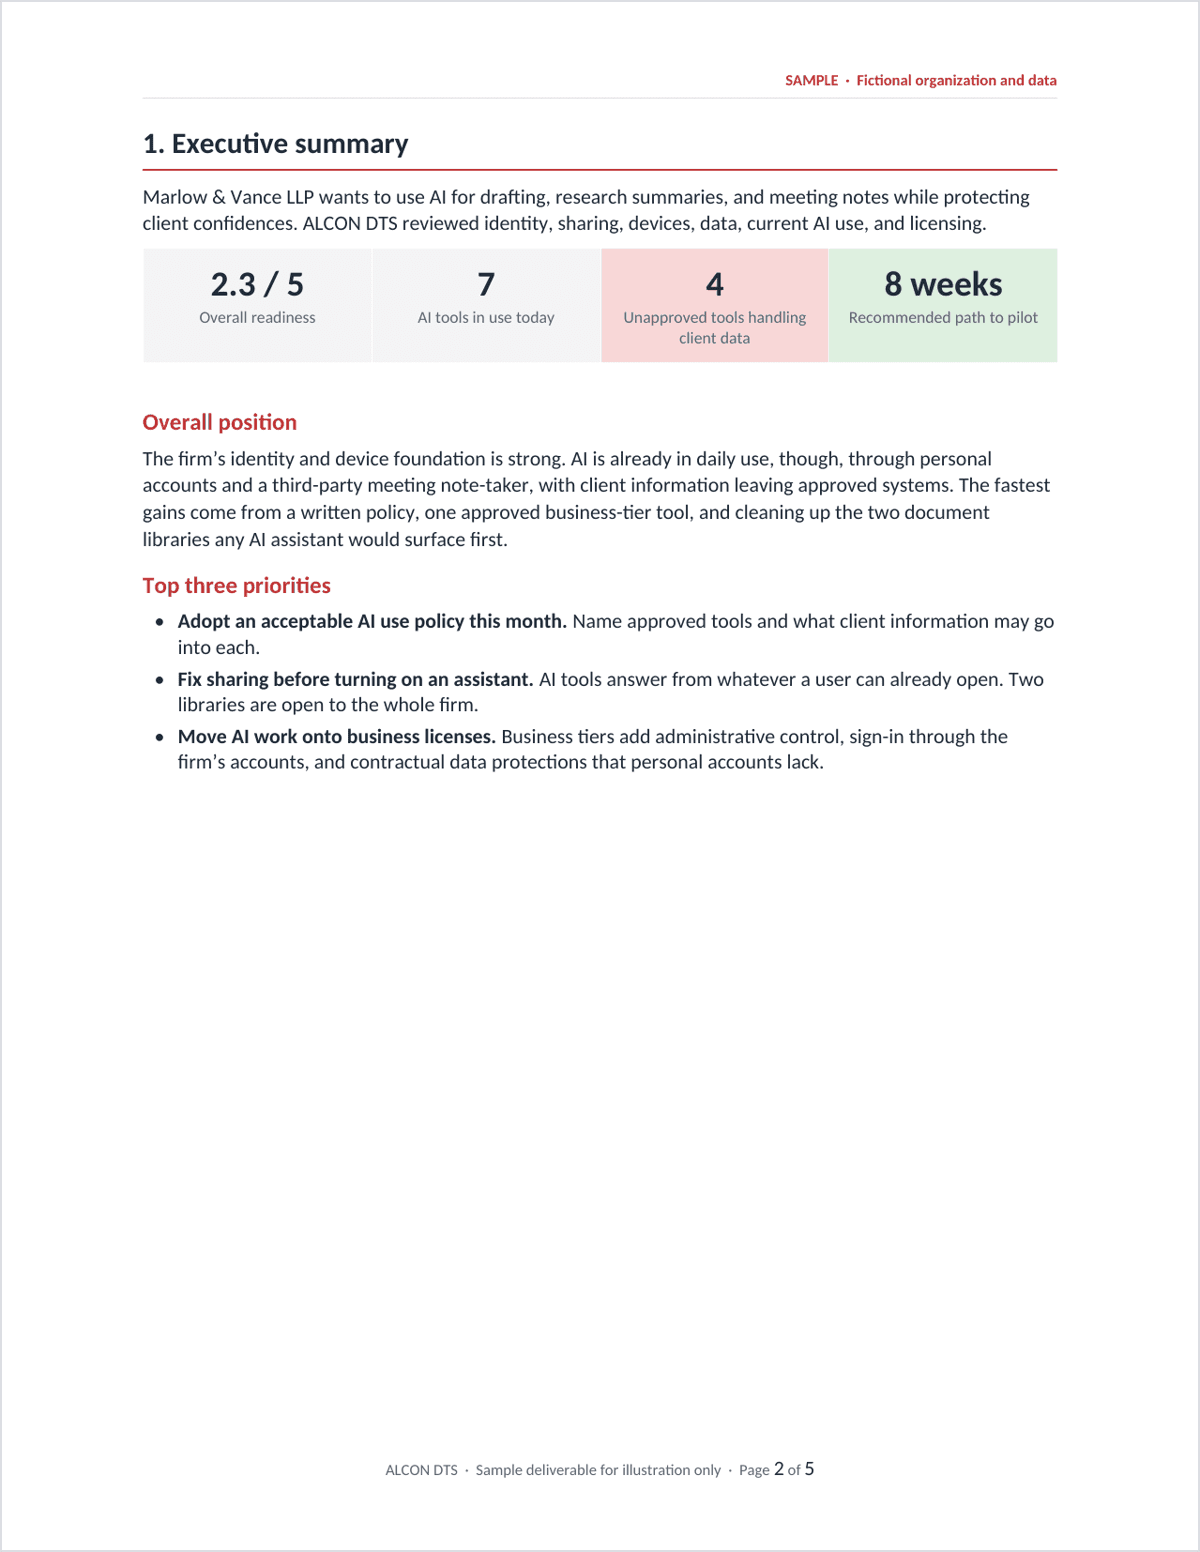
See the format and depth of what ALCON DTS clients receive.
 Guide
Texas SB 2610 bars punitive damages in breach suits for businesses under 250 employees with a framework-based security program.
 Guide
What SB 1188 and HB 149 require when clinics use AI: patient disclosure, practitioner review, and U.S. storage of health records.
 Guide
A HIPAA security risk analysis is required for covered entities and business associates.
 Guide
Who the thresholds catch, what a request path has to do, and what ALCON DTS does not decide.
 Guide
CMMC can apply to DoD contractors and suppliers that handle FCI or CUI.
 Guide
Texas law requires breach notice to individuals within 60 days and to the Attorney General within 30 days for 250 or more Texans.
 Guide
HIPAA requires a business associate agreement before a vendor handles patient information.
 Guide
CIS Controls IG1 is 56 essential Safeguards in CIS Controls v8.1.
 Guide
NIST CSF 2.0 organizes security into six Functions, including Govern.
 Guide
Get your Microsoft 365 environment ready for Microsoft Copilot: fix oversharing, apply sensitivity labels, confirm licenses and plan a pilot before rollout.
 Guide
Keeping patient data in Microsoft 365? See what Microsoft’s BAA covers, what you configure, and how MFA, encryption, audit logs and sharing map to HIPAA.
 Guide
Which MFA methods resist phishing, how Conditional Access and legacy sign-in blocking work, break-glass accounts, and how MFA maps to HIPAA, CMMC and CIS IG1.
 Guide
How to answer SIG, CAIQ, HECVAT and cyber insurance questionnaires honestly, what evidence to keep, and how ALCON DTS can help draft technical answers.
 Guide
What a customer is asking for, who issues the report, and what ALCON DTS does not sign.
 Guide
What the payment standard covers, who decides the questionnaire, and what ALCON DTS does not attest.
 Guide
Who NERC CIP covers, how CIP-002 impact categories work, which versions are in force, what is changing through 2029 and how enforcement works.
NERC CIP ERCOT PUCT Texas grid energy utilities
 Guide
Texas grid cyber rules: the PUCT cybersecurity monitor, Emergency Operations Plan cyber annex, ERCOT incident notice, LISPA and PUCT penalties.
NERC CIP ERCOT PUCT Texas grid energy utilities
 Guide
The first steps to take after a cyber incident, the five CISA response phases, containment trade-offs, Texas breach notice timing and what to have ready.
incident response cyber attack cyberattack ransomware data breach security hacked compromised account business email compromise phishing malware CISA playbook plan first hour what do after containment eradication recovery NIST SP 800-61 CSF tabletop exercise backups vulnerability known exploited vulnerabilities KEV Texas notification Attorney General 521.053 FBI IC3 CIRCIA insurance evidence forensics
Based in Austin, Texas, since 2001. Managed IT, cybersecurity, and compliance for organizations across the U.S.

© 2026 ALCON DTS.